Cybersecurity has changed dramatically over the past three decades. The web arrived, phones
became smart, everything moved to the cloud, and now AI is reshaping the landscape once again. And yet, according to Steven Furnell, Professor of Cyber Security at the University of
Nottingham, some things haven’t changed nearly enough.
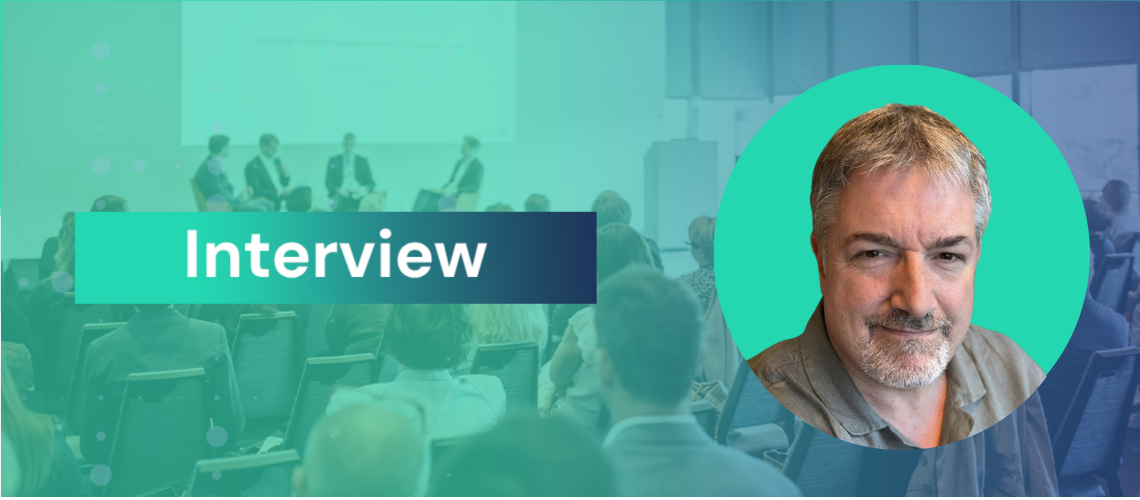
Steven joined us at EAI SecureComm 2026 as a keynote speaker, where his talk Protecting
the Human Endpoint explored an idea that has followed him throughout much of his career:
security isn’t only about technology. It is about the people who are expected to use it.
For this edition of Voices of EAI, we spoke with Steven about his journey through
cybersecurity, why we should stop simply blaming users, the importance of research
communities, and what decades of studying technology and human behavior have taught him.
From computer security to cybersecurity
Steven entered the field almost by accident.
After completing his undergraduate degree in computing, he came across a funded PhD
opportunity focused on computer and data security in healthcare. Security hadn’t been his
original plan, but it didn’t take long for the subject to draw him in.
His early research eventually led him to keystroke dynamics – authenticating people through the way they type. What interested him was not only whether the technology worked, but whether the security could operate without constantly getting in the user’s way.
That question has remained surprisingly relevant. In fact, when we asked Steven what had
surprised him most about cybersecurity’s evolution, his answer wasn’t how much had changed.
It was how much hadn’t.
Passwords are a perfect example. Their weaknesses were well understood when Steven began
his PhD, yet decades later, passwords such as “123456” continue to appear among the world’s
most commonly used each year. But Steven isn’t interested in simply blaming people. If systems continue allowing users to choose passwords we have known to be weak for decades, he argues, perhaps the question shouldn’t only be why are users still doing this?
It should also be: why are we still letting them?
Protecting the human endpoint
That thinking sits at the heart of Steven’s SecureComm keynote, Protecting the Human
Endpoint.
Every new generation of technology brings new possibilities and new vulnerabilities. But one
element remains consistent: the person using it.
“Every encounter we have with security has the potential to put us off or be negative or feel like a barrier”, Steven explained.
Security measures often ask people to do more, remember more, and interrupt whatever they were actually trying to accomplish. For Steven, that means usability cannot be an afterthought. The same applies to cybersecurity awareness. An organization can require employees to complete annual training and tick the compliance box, but that doesn’t necessarily mean anyone’s behavior has changed.
So, after studying humans and cybersecurity for all these years, we had to ask: is there still hope for us?
“Absolutely.”
Steven remains optimistic about people. Most aren’t actively working against security; they want to be protected. The challenge is making the secure choice reasonable and accessible rather than placing unnecessary barriers in their way.
And unless, as Steven joked, “the machines take over with all the AI stuff,” there are still plenty
of reasons for optimism.
Why research communities still matter
Technology may enable us to collaborate from almost anywhere, but Steven remains a firm
believer in meeting face-to-face.
Conferences such as EAI SecureComm, he says, create a space where new research can be
shared, challenged and ultimately become part of the wider knowledge of the field. Some ideas remain academic; others may eventually become the foundations of technologies and services we use every day.
But the value goes beyond presenting a paper. The conversations afterwards, the coffee breaks and the unexpected connections are often where new relationships and collaborations begin.
As Steven put it, an online conference can deliver the presentations and even provide a good delegate experience
“But it doesn’t deliver coffee.”
For someone who has seen conferences move online and back again, Steven believes that human connection remains difficult to replicate digitally. At the same time, he sees real value in what the pandemic accelerated:
“hybrid participation can open research communities to people who otherwise might never have been able to join them“.
Find something you actually enjoy
We end every Voices of EAI conversation with the same question: what advice would you
give to young researchers?
Steven’s answer was refreshingly simple: Find something you’re genuinely interested in. Don’t chase an area purely because it seems fashionable, because someone else tells you to, or because you think that’s where the money is. Find the intersection between what interests you and what you’re good at.
Steven readily admits that this wasn’t exactly the result of a carefully constructed career plan in his own case.
“I just fell into it and carried on doing it.”
But somewhere along the way, he found his space.
And that, he believes, matters. If you’re already bored by your chosen subject at the beginning, it probably isn’t something you should spend years pursuing
Think before you act
Before we let Steven go, we asked one final question: if you could patch one human behaviour the way we patch software, what would you fix?
His answer brought the conversation neatly back to where it started:
“Think before you act.”
Pause before clicking the suspicious link. Before choosing the weak password. Before ignoring the update. Not every cybersecurity problem requires another layer of complicated technology. Sometimes, a moment of thought can make all the difference.
And perhaps that explains why, after all these years, Steven remains fascinated by both technology and the people using it.
The technology will keep changing. New vulnerabilities will emerge, new research will respond, and research communities like SecureComm will continue bringing together the people working on what comes next.